
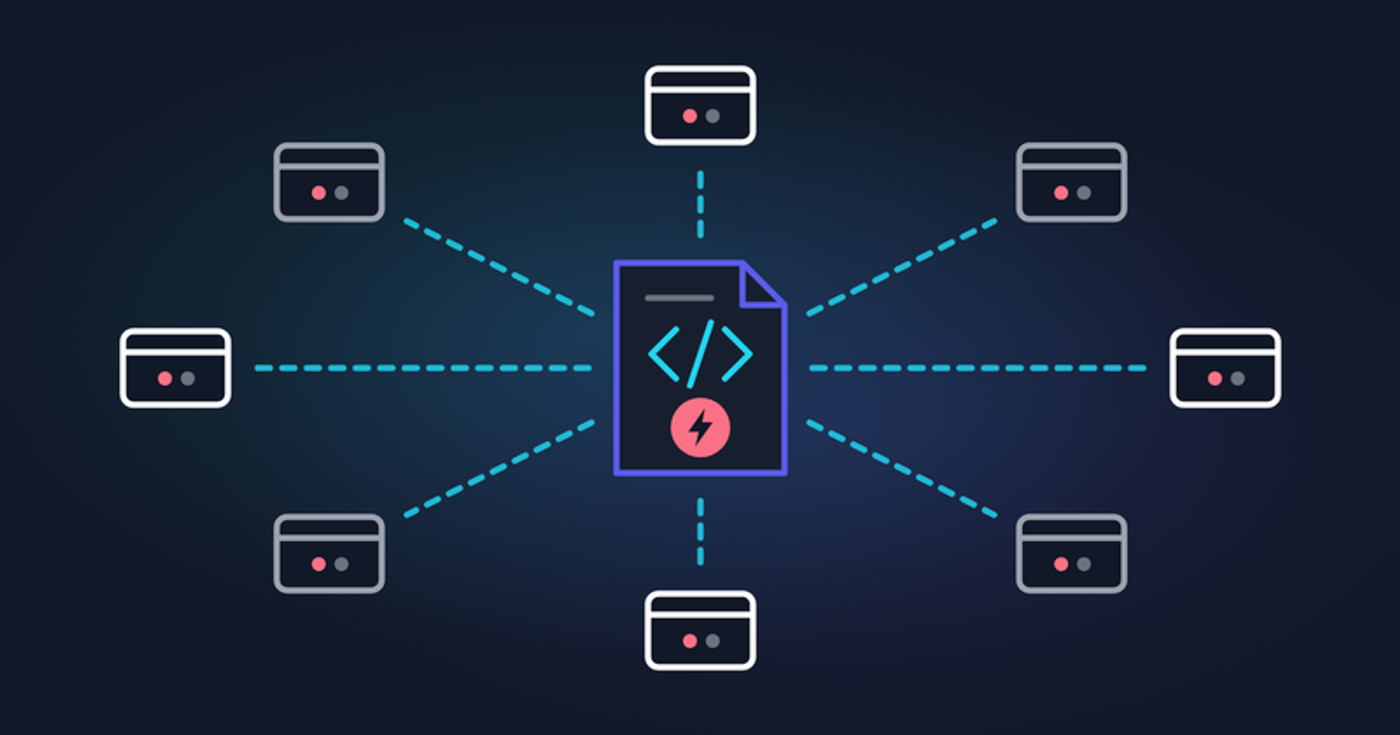
On November 16, 2026, one compromised vendor script turned the websites of at least 178 organizations, including Zoom, the BBC, CNN, HSBC, Equifax, and Salesforce, into card skimming and crypto theft platforms for most of a day. None had their servers breached.
The affected websites loaded a trusted A/B testing snippet from Optimizely, and the attacker rewrote what that snippet did. That snippet is served from Cloudflare's network, and by Optimizely's own account, the malicious code was delivered through Cloudflare.
Allowlisting the vendor's domain did nothing, and only 24 of the 159 affected organizations whose policies Report URI could classify (15%) had a Content Security Policy strict enough to block the payload.
What happened
An attacker abused a flaw in Optimizely's account signup flow to impersonate users on customer accounts and edit Project JavaScript, a field that runs on every page the snippet loads (Rescana). The attacker added a small loader and changed nothing else, so the file still came from cdn.optimizely.com with a valid certificate. Report URI found malicious code in 188 of 1,611 snippets it checked; the payload was rebuilt 26 times between the first injection at 04:21 UTC and cleanup at 23:11 UTC (Report URI). Optimizely says the attack even bypassed its PCI-designated host, cdn-pci.optimizely.com.
How the card skimmer worked
The card module watched form submissions for a Luhn valid card number, expiry date and CVV, then beaconed them to the attacker's server at 1688360.cc. No server, database or web application firewall at any affected company saw the data leave. It went straight from the shopper's browser to the attacker.
The rest of the kit
Sites with no checkout were still hit. The same toolkit swapped crypto wallet addresses, stole cookies and screenshots, and pushed the DarkSword and Coruna exploit chains to older iPhones and iPads (KrebsOnSecurity). PCI DSS scopes its script controls to payment pages, so none of that falls under them.
Why the usual defenses missed it
- Firewalls never saw it. The code went from the vendor's CDN straight to the browser.
- CSP trusted the source. Of 159 organizations whose policies Report URI classified, 68 had no CSP and only 24 blocked the payload. 'strict-dynamic' and 'unsafe-eval' (which Optimizely's documentation recommends) let it through.
- Subresource Integrity (SRI) could not apply. There is no stable hash for a snippet that changes whenever marketing edits a test (W3C Subresource Integrity spec).
- PCI DSS 11.6.1 allows weekly tamper checks. A weekly check would likely have missed an injection that lasted less than a day (Rescana).
Would Cloudflare or Akamai have stopped it?
Cloudflare was in the delivery path, not the protection path. Optimizely told KrebsOnSecurity it had "implemented additional protections to prevent malicious code from being delivered in Cloudflare" (KrebsOnSecurity, BleepingComputer). The infrastructure confirms it: cdn.optimizely.com resolves to Cloudflare's content delivery network on Cloudflare Anycast IP addresses (checked November 18, 2026). Optimizely blocked the code at its Cloudflare edge only after it had detected the attack, and Report URI still found infected snippets after that block (Rescana).
Cloudflare also sells Client-Side Security (formerly Page Shield) for sites it fronts. Nothing published shows whether any affected site ran it, but its design explains why it would have struggled:
- It trusts by source. Its blocking trusts by source. cdn.optimizely.com was already allowed everywhere, and its content security rules are CSP allowlists.
- It samples. Cloudflare's documentation says its script list is based on sampling, with a delay before new scripts appear (Cloudflare).
- Real detection costs extra. Malicious script and code change detection sit only in the paid Client-Side Security Advanced tier (Cloudflare).
- Change alerts meet a script built to change. A payload rebuilt 26 times in a day reads as noise.
Akamai's client side product is likely a better fit as it watches script behavior in real sessions and can enforce policies against exfiltration (Akamai). But it runs as JavaScript in the same page as the attacker, and its blocking depends on behavior policies being in place before the attack.
Both watch scripts from inside a browser the attacker already controls. Checking every script before it reaches the browser, and keeping the card number out of the page altogether, is what stops the flood.
What actually breaks the attack: make card data worthless before scripts see it
A skimmer can only steal what the page can read. Detection tools race the attacker but DataStealth takes the card number off the table. DataStealth is a Data Security Platform built on Zero Trust, and three of its products work together on the payment page, each closing a gap the Optimizely attack exploited.
- Payment card tokenization. DataStealth replaces the card number with a format-preserving token, in real time, inline, with no agents and no changes to your back-end applications. Downstream systems only ever handle a substitute value that is worthless to an attacker.
- eSkimming protection. DataStealth controls which scripts may run on your payment pages and alerts on unauthorized changes to them, giving you the script inventory, authorization and tamper detection that PCI DSS 6.4.3 and 11.6.1 require. Trust is not granted on the strength of a domain, so a trusted vendor suddenly serving new code is treated as a change, not a given.
- iframe protection. Hosted payment fields were the control that held on November 16, but iframes have attacks of their own: overlays, fake forms and hijacked frames. DataStealth iframe protection guards the payment iframe and the page around it, so the field your customer types into is the real one. With DataStealth hosted fields, the card number and CVV are tokenized inside the frame, so the page only ever receives a token.
Together, the card number is captured in a field no page script can read, the scripts on the page are authorized and checked on every load, and only verified payment frames can render. Pair that with basic hygiene: no experimentation or analytics tags on checkout or login, and a strict CSP as a backstop.
That is the difference between hoping to notice a skimmer and making sure it has nothing worth stealing.
What to do this week
- Optimizely customers: audit Project JavaScript for 1688360.cc, atob( and eval; review changes made November 13 to 17; treat November 16 card data as exposed and brief your acquirer and QSA; invalidate session cookies not marked HttpOnly.
- Anyone with a payment page: justify every script on it, know where the card number is typed, and ask your client-side vendor what stops the data leaving when a trusted script turns.
- Visitors to affected sites: update iPhones and iPads, and check card statements.
Review your data protection strategy before the next trusted script turns
The Optimizely attack won’t be the last time a trusted script turns, so the useful question is what your payment pages would have exposed on November 16 and where else your sensitive data can still be read.
We’ll map where card data and other sensitive data are exposed today, from the checkout page to the systems behind it, and show how tokenization takes that data off the table.
Book a demo with our team to get started.
Ed Leavens is the Chief Strategic Officer, co-founder and former CEO at DataStealth.io and a cybersecurity innovator.
Connect on LinkedIn →